Is this the official HHS Security Risk Assessment Tool?
No. Our assessment follows the structure of the HHS/ONC SRA Tool and cites the Security Rule throughout, but it is built and supported by NBT Systems and is not endorsed by HHS.
How often do we need a risk analysis?
The Security Rule treats risk analysis as an ongoing process: review it regularly and update it when your systems, locations or operations change. Clinicians reporting MIPS Promoting Interoperability must conduct or review one during each performance year. Most practices assess annually.
Does my information leave my computer?
For the free assessment, no. Your answers are stored only in your browser until you save a progress file. With Option 2, you choose to send that file to us. Please don’t include patient names or other patient information in your notes.
Can I see what a report looks like?
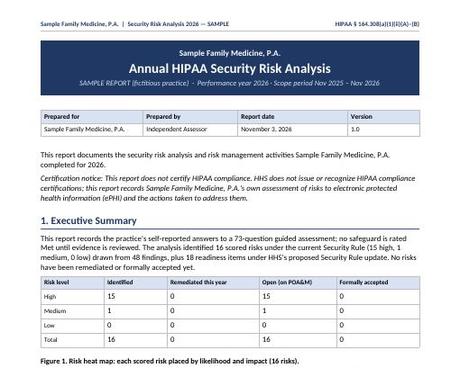
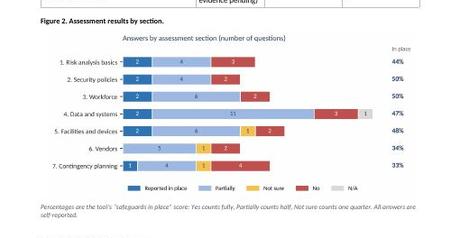
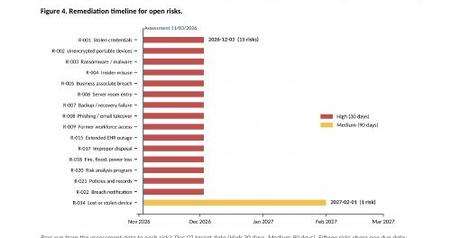
Yes. Download our sample Security Risk Analysis report for a fictitious practice. It shows the findings, risk register, remediation plan and figures you can expect.
How are reports and documents prepared?
Option 2 reports are drafted with AI assistance from the answers in your progress file, using NBT Systems templates, and are not reviewed or validated, so their accuracy depends on your answers. Diagrams are conceptual, based on what you describe. In the NBT Systems-guided engagement, a security professional reviews your answers, validates your safeguards and diagrams, and finalizes the report.
What’s the difference between Option 2 and Option 3?
Option 2 turns what you report into a formal Security Risk Analysis report, generated from your answers without review. Option 3 is a full professional engagement: we interview your team, review evidence, validate technical controls and produce a formal Security Risk Analysis report. If you need documentation that holds up to an audit or investigation, Option 3 is the stronger choice.
If we start with the $399 report, can we upgrade later?
Yes. If you move to the NBT Systems-guided engagement within 60 days of ordering your report, the full $399 is credited toward it. Your answers carry over, so nothing is wasted.
We have more than 20 staff or several locations. Can you help?
Yes. Option 3 pricing scales with practice size and complexity. Book a consultation and we’ll provide a quote.
Is the engagement on site?
Option 3 is delivered remotely through video interviews, screen sharing and secure document exchange, which keeps it efficient and affordable.
Can the assessment help with our cyber insurance?
It can help, though no assessment guarantees a lower premium. Cyber insurers now ask detailed questions about many of the same controls the assessment covers, including multi-factor authentication, endpoint protection, tested backups, patching, email security and an incident response plan. Gaps in those controls can lead to higher premiums, coverage exclusions or a declined application. The assessment shows where you stand before you apply or renew, and an NBT Systems report or engagement gives you a prioritized plan for closing the gaps underwriters care about most. Always answer insurance applications accurately: a claim can be disputed if a control you reported wasn’t actually in place.
Does completing the assessment make us HIPAA compliant?
No assessment alone guarantees compliance. The risk analysis identifies what needs attention; compliance comes from acting on the findings and maintaining your security program over time.